Customer data security for aesthetic clinics under the 2026 data law
From 1 January 2026, customers' health information, treatment photos and phone numbers are protected by the Law on Personal Data Protection. How should clinics obtain consent, are they exempt, how large are the fines, and what should they do first?
From 1 January 2026, customer data security at aesthetic clinics is a legal obligation under the Law on Personal Data Protection No. 91/2025/QH15: customers' health information is sensitive data, collecting it requires clear consent for each purpose, and violations can be fined up to VND 3 billion. This article summarizes what clinics and spas need to know, the specific fines under the new decree, and 10 things to do first.
Which regulations currently apply?
Document | Main content | Effective from |
|---|---|---|
General legal framework: consent, customer rights, business obligations, maximum fines | 1 January 2026 | |
Detailed guidance, list of sensitive data, how to obtain consent | 1 January 2026 | |
Specific fines for each violation | 19 August 2026 | |
Patients have the right to confidentiality of the information in their medical records | 1 January 2024 |
Decree 13/2023/ND-CP on personal data protection ceased to be effective on 1 January 2026. Consent that customers gave under Decree 13 remains valid, so clinics do not need to ask for it again.
Which customer data is sensitive data?
The Law divides personal data into two types: basic and sensitive. Sensitive data carries stricter obligations, and aesthetic clinics process this type of data every day.
Customer information | Type under Decree 356/2025 | Notes |
|---|---|---|
Full name, phone number, personal identification number | Basic | |
Images of the customer | Basic | Before-and-after treatment photos show skin condition and treatment, so handle them as sensitive data |
Health condition, medical history, allergies, diagnosis | Sensitive | |
Biometric data (fingerprints, faces used for identification) | Sensitive | |
ID card images, bank card details | Sensitive |
Treating before-and-after photos as sensitive data is a cautious interpretation, not the wording of the decree. For clinics, though, it is the safest approach, because those photos are tied to the customer's health condition and treatment.
When is a customer's consent valid?
Under the Law (Article 9) and Decree 356/2025 (Article 6), consent is valid only when it is:
Voluntary and informed: the customer knows the type of data, the purpose, who processes it and their own rights. For sensitive data, the customer must be clearly told that it is sensitive data.
Given for each purpose: consent to treatment does not mean consent to advertising. Several purposes may not be bundled into one signature.
Verifiable: in writing, by text message, by email, by recorded call, or through a mechanism on a website or app. The clinic must keep the evidence.
Never silent, never pre-ticked: silence or no response is not considered consent, and pre-ticked consent boxes are prohibited.
For health information specifically, the Law (Article 26) requires the customer's consent to collect and process it, except in certain cases such as emergencies. Clinics also may not transfer a customer's data to another healthcare facility or an insurance company unless the customer requests it in writing.
The table below suggests how to separate purposes when drafting a consent form:
Purpose | Separate consent needed? |
|---|---|
Examination, treatment, keeping records | Yes, because it involves health information |
Taking and storing before-and-after photos to monitor treatment | Yes |
Appointment reminders, aftercare | Recommended; state the contact channel clearly |
Sending promotional messages | Yes, kept separate from the treatment purpose |
Using photos in advertising | Yes, kept separate; under the Civil Code (Article 32), using a person's image for commercial purposes requires paying the person in the photo, unless the two parties agree otherwise |
Are small clinics exempt?
This is a point many people misunderstand. The Law lets small businesses and start-ups choose whether or not to apply certain obligations for 5 years, and exempts household businesses and micro-enterprises, but only for two obligations: preparing an impact assessment dossier and appointing a person in charge of data protection.
More importantly, this exemption does not apply to facilities that directly process sensitive personal data (dữ liệu cá nhân nhạy cảm). Clinics process customers' health information, so they almost certainly belong to the group that must:
Prepare a personal data processing impact assessment dossier and send it to the specialized personal data protection agency (Ministry of Public Security) within 60 days of starting processing.
Appoint a department or person qualified to protect personal data, or hire an organization or individual that provides this service. Under Decree 356/2025, the appointed person needs a college degree or higher, at least 2 years of relevant experience, and training in personal data protection.
The remaining obligations, such as obtaining consent, keeping data secure and reporting incidents, apply to every facility, including spas and household businesses.
How large are the fines?
The Law sets a maximum fine of VND 3 billion for most violations, up to 10 times the revenue earned from buying and selling data, and up to 5% of the previous year's revenue only for violations involving transferring data abroad. Decree 330/2026/ND-CP sets out the specific fines. Below are some violations clinics are likely to run into (fines for individuals are half these amounts):
Violation | Fine for organizations |
|---|---|
Processing data without valid consent, using pre-ticked boxes, not keeping evidence of consent | VND 30–50 million |
Treating silence as consent, continuing to process data after the customer has objected | VND 50–70 million |
Publishing personal data (for example, posting customer photos) without consent | VND 30–50 million, plus mandatory removal |
Not preparing or not submitting the impact assessment dossier within 60 days | VND 20–30 million |
Not appointing a person in charge of data protection in writing | VND 20–30 million |
Transferring patient data to another healthcare facility or an insurance company when the customer has not requested it in writing | VND 70–100 million, plus 3–6 months' suspension |
Using sensitive data to run targeted advertising without consent | VND 50–70 million |
If a data breach occurs that could harm a customer's life, health, honor or property, the clinic must notify the specialized agency within 72 hours at the latest.
Customer data security day to day: permissions and logs
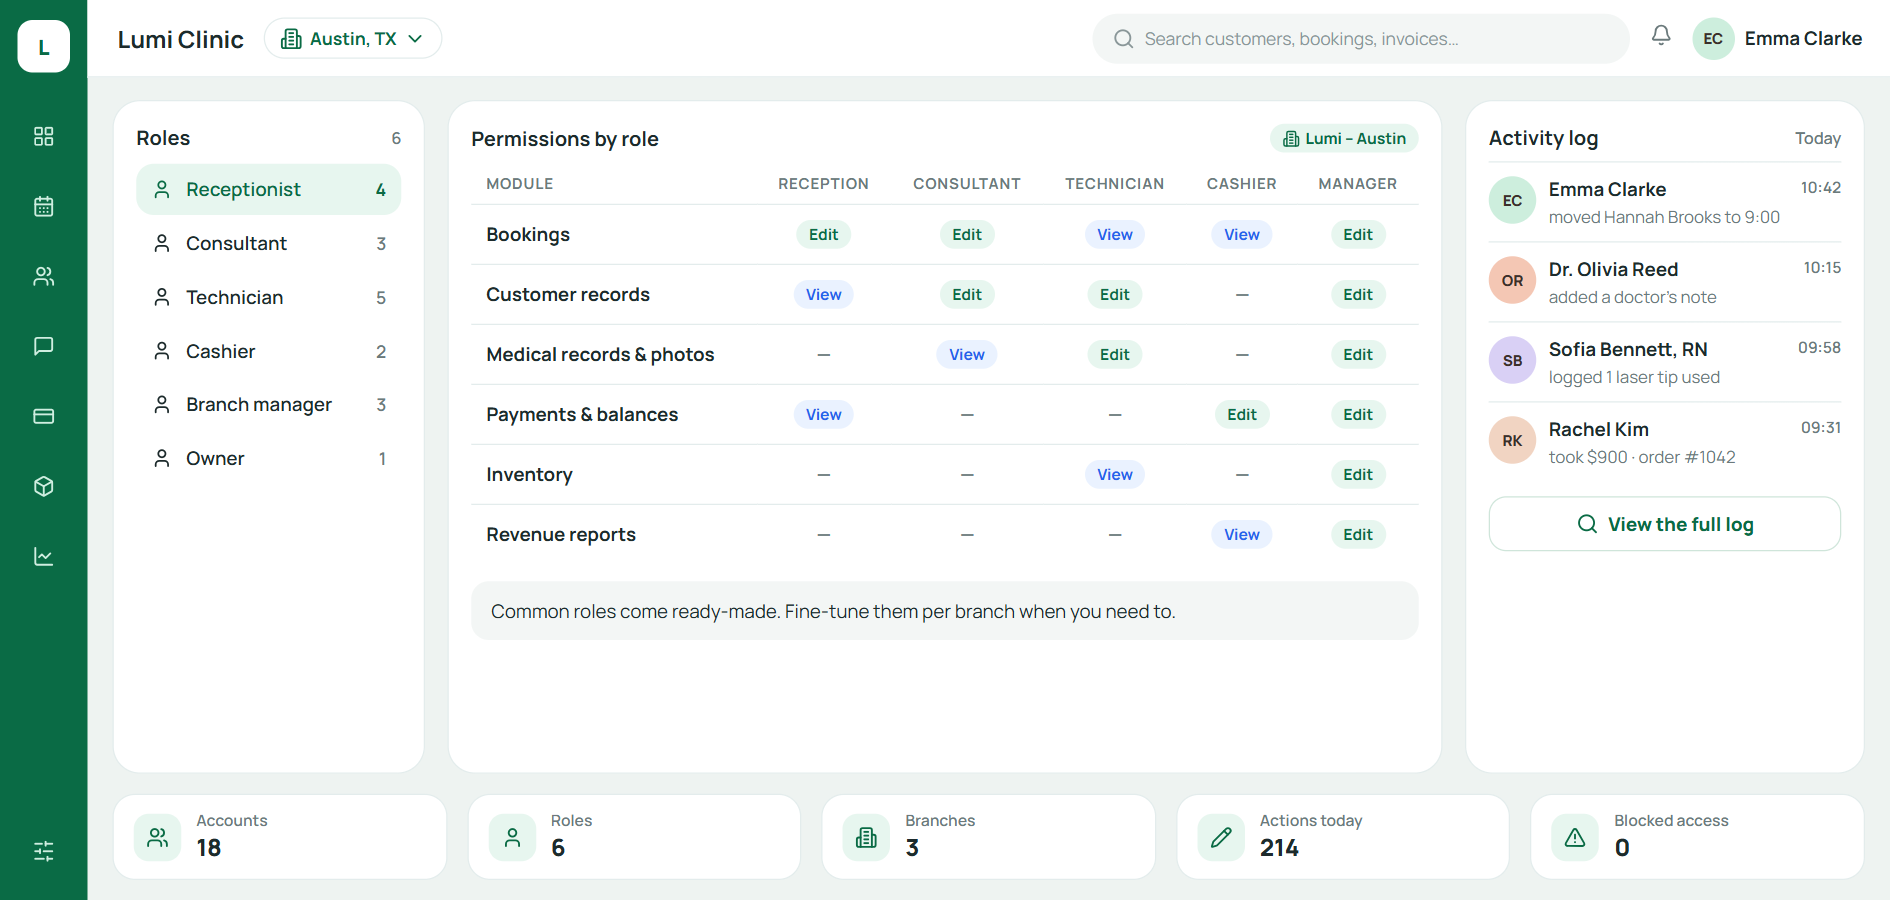
The Law sets the obligations, but customer data security day to day depends on how the clinic operates. The most common risk is not hackers. It is data sitting on staff members' personal phones, Excel files sent around in group chats, or shared accounts where anyone can see everything.
The basic principle is that each person sees only the data they need for their own work:
Receptionists see schedules and contact details, but not treatment forms or photos.
Consultants see the conversations and needs of the customers they look after.
Doctors and technicians see the treatment records of customers in their own shift.
Branch managers see their own branch's data, but not other branches'.
Every time customer data is viewed, edited, exported or deleted, the action should be logged with who did it and when. This log helps detect incidents and also serves as evidence that the clinic has protective measures in place. Our article on spa customer records management suggests who should see which groups of information.
10 things clinics should do now
List the data you collect, where it is stored and who can see it.
Rewrite your consent form so that each purpose is separate and sensitive data is clearly identified.
Keep evidence of each customer's consent, and do not use pre-ticked boxes.
Prepare the impact assessment dossier and submit it within 60 days.
Appoint a person in charge of data protection in writing, or hire a service.
Give each staff member their own account, and lock it as soon as they leave.
Do not consult with customers or store their photos on personal devices and accounts.
Set permissions by role and by branch, and turn on activity logs.
Export data only when necessary and with someone's approval.
Write an incident response procedure in advance, so you can notify within 72 hours.
Permissions and logs are the part that needs a supporting tool. Qub-X is one option, with permissions by role and by branch, plus activity logs on customer data. For licensed clinics, see also the security requirements for EMR for aesthetic clinics.
Frequently asked questions
Do spas have to comply with the Law on Personal Data Protection?
Yes. The Law applies to every organization and individual that processes personal data, including spas and household businesses. If a spa stores information about customers' skin condition, allergies or health, it should handle that information as sensitive data.
Do customers who consented under Decree 13/2023 need to consent again?
No. Consent obtained under Decree 13/2023/ND-CP remains valid. From now on, new consent requests must follow the Law and Decree 356/2025.
Do I need consent to send promotions to past customers?
Yes. Advertising and promotions are a separate purpose from treatment and care. Ask for separate consent for this purpose and give customers an easy way to opt out of messages.
What do I need before posting a customer's before-and-after photos on social media?
You need the customer's separate consent to use the photos in advertising, with evidence kept on file, and an agreement on payment, if any. Publishing photos without consent can be fined VND 30–50 million for organizations, with mandatory removal.
Sources
Civil Code 2015 (Official Gazette) (in Vietnamese)
This article summarizes documents issued up to October 2026. It is for reference only and does not replace legal advice. Clinics should consult a lawyer when drafting consent forms and impact assessment dossiers.
Related articles
All articles on Security & compliance- Security & compliance
EMR Software That Meets Vietnam Ministry of Health Standards
The 31 December 2026 deadline is close for every licensed clinic. This guide helps aesthetic and dermatology clinics understand what the Ministry of Health requires and choose software that gets them there in time.
- Clinic operations
Why Beauty Salon Management Software From Qub-X Matters
Messages in several apps, appointments in a notebook and client history on staff phones make it hard for spas and beauty salons to follow each client. This is the role of one central management platform.
- Customer care
Spa customer retention: 8 ways to bring clients back a second time
New clients take effort to find; returning clients are what build lasting revenue. Here is how to measure your return rate, a 30-day aftercare schedule and 8 things your spa should start doing now.